Fortinet Security Fabric Repair:
FortiGate, FortiAP, FortiSwitch, FortiAnalyzer.
Fortinet FortiGate dominates NYC SMB and mid-market firewalling because of its UTM feature density, Security Fabric integration, and significantly lower pricing per feature than Cisco ASA or Palo Alto. Heavy install base in NYC medical offices, mid-size law firms, retail chains, and property management companies. We service the full fabric: FortiGate, FortiAP, FortiSwitch, FortiAnalyzer, FortiManager.
Where Fortinet Lives in NYC
FortiGate dominates NYC SMB and mid-market firewalling because of its UTM feature density, Security Fabric integration across firewall/switch/AP/EDR, and significantly lower pricing per feature than Cisco ASA or Palo Alto. The install base is heavy in NYC medical offices, mid-size law firms, retail chains, and property management companies.
The service story centers on subscription discipline and security posture. FortiGuard subscriptions gate IPS, antivirus, web filtering, and FortiCare support. When they lapse the firewall keeps passing traffic but security degrades invisibly. SSL VPN brute-force exposure after the 2022-2024 Fortinet CVEs is a recurring theme on exposed FortiGates.
The Fortinet Hardware in NYC
Across the FortiGate range plus the Security Fabric peripherals.
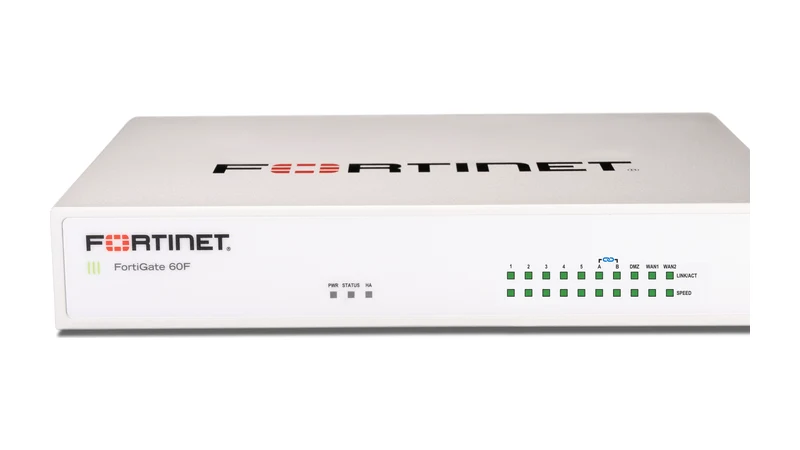
FortiGate Firewalls
Flagship UTM firewalls with built-in VPN, IPS, antivirus, web filtering, SD-WAN. Covers the full NYC SMB range from solo-practice medical offices to multi-tenant commercial.
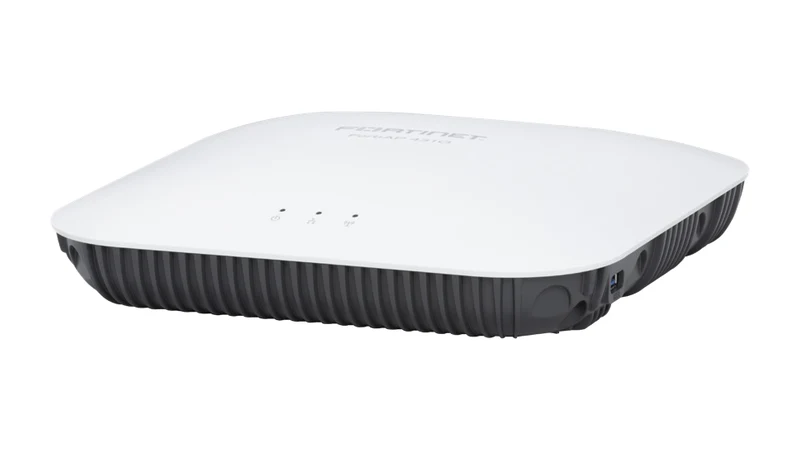
FortiAP (Wi-Fi Access Points)
Managed access points integrated with FortiGate controller function. Positioned as the all-Fortinet alternative for sites already running FortiGate.
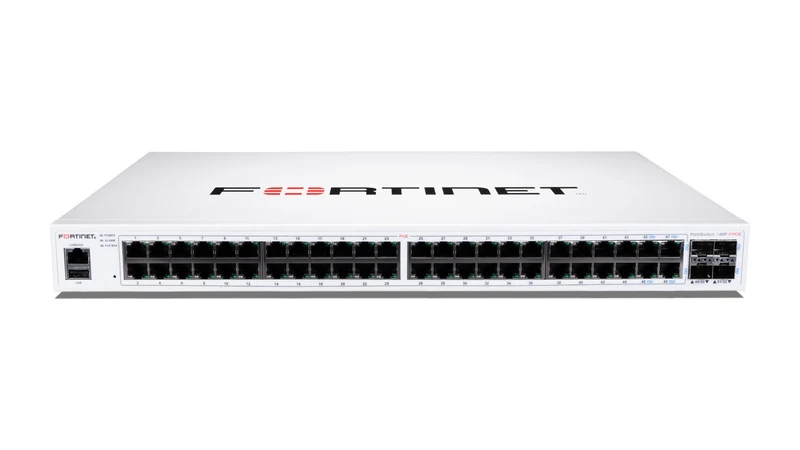
FortiSwitch (managed Ethernet switching)
Managed access and distribution switches controlled directly from FortiGate via FortiLink, letting the firewall manage the LAN.
FortiExtender (5G and LTE WAN)
LTE and 5G WAN appliances for failover or primary internet. Deployed in NYC medical and legal practices where downtime equals revenue loss.
FortiAnalyzer / FortiManager
Centralized log aggregation (FortiAnalyzer) and policy management (FortiManager) for multi-FortiGate deployments. Common at property management firms with 10+ sites.
What We See in the Field
Fortinet failures cluster around subscription lapse and SSL VPN exposure more than hardware failure.
Expired FortiGuard subscription silently degrades protection
IPS signatures, antivirus definitions, and web filter categories stop updating when FortiGuard lapses. Firewall continues passing traffic but security posture degrades invisibly, often for 6+ months before an incident reveals it.
Affects: FortiGate 40F through 400F
SSL VPN brute-force attempts and the move to IPsec
High-profile Fortinet CVEs in 2022-2024 drive attackers to constantly brute-force SSL VPN on exposed FortiGates. On FortiOS 7.6, SSL VPN is no longer available at all on 2GB models such as the 40F and 60F, so remote access has to move to IPsec VPN.
Affects: FortiGate 40F, 60F, and any FortiGate with SSL VPN exposed
FortiLink desync between FortiGate and FortiSwitch
FortiSwitch loses management link to FortiGate during firmware upgrade and reverts to standalone mode, with VLAN config no longer synced from the firewall. Users notice broken VLAN membership and VoIP outages.
Affects: FortiSwitch 108E, 148F, 248D managed by FortiGate 60F/100F/200F
HA pair split-brain after firmware mismatch
HA cluster where primary gets upgraded and secondary does not, resulting in both claiming active state and MAC flapping on the network. Common when upgrades are rushed outside maintenance windows.
Affects: FortiGate 60F through 400F in HA pairs
Logs filling up on small FortiGates
The FortiGate 60F has no internal log disk (the 61F adds one), so busy small units run short on log space. Sending logs to FortiAnalyzer or FortiCloud keeps history without straining the firewall.
Affects: FortiGate 40F, 60F, 60E
Admin lockout after password rotation
IT rotates the admin password, the new one is not recorded, and nobody can log in. On firmware older than FortiOS 7.2.4 the console maintainer login recovers it. On 7.2.4 and later the maintainer account is gone, and recovery needs a config backup and console access.
Affects: All FortiGate models
The Service Specifics
Fortinet licensing is subscription-driven: FortiGuard subscriptions (Advanced Threat Protection, Unified Threat Protection, Enterprise Protection) gate IPS, AV, web filtering, and FortiCare support. Letting them lapse keeps the firewall functional but drops security posture significantly.
Cloud dependencies include FortiCloud for log retention and FortiAnalyzer-as-a-service. The firewalls themselves run fully offline. Admin recovery on orphaned FortiGates needs console access: the maintainer login on firmware older than FortiOS 7.2.4, or a config backup with the password removed on 7.2.4 and later.
The Legacy Install Base
Legacy FortiGate hardware still common in NYC SMB.
FortiGate 60D / 90D / 100D
Pre-FortiOS 7 era hardware, no longer receiving major firmware. Still deployed at NYC medical offices and small law firms.
FortiWiFi 60D
Integrated wireless FortiGate from the FortiOS 6 era. End of sale, still found in solo-practice offices.
FortiAP 221C / 223C / 320C
Pre-Wi-Fi 6 APs running on older FortiOS controller firmware.
Older FortiAnalyzer appliances
Early appliance-based log collectors, replaced by current F and G series models such as the FortiAnalyzer 300F and 150G.
If Your Specific Problem Is...
For a specific Fortinet symptom, these are the pages you want.
Network Down / No Internet
FortiGate firewall or ISP integration failure. Priority dispatch.
Outage repair → 02 / SymptomSlow Network / Bottlenecks
FortiGate throughput cap or feature processing bottleneck.
Slow network → 03 / SymptomWi-Fi Dead Zones
FortiAP coverage or FortiLink desync problems.
Wi-Fi repair →Fortinet Repair FAQ
Fortinet Install Need Service? We will Keep It Secure.
Any FortiGate model, FortiGuard reinstated, HA restored, fabric-integrated. Licensed and insured.